Prove Your Controls Work
SOC 2 Consultants in India: Readiness and Audit
SOC 2 is the attestation report customers ask for before they trust you with their data. We help you get ready for both Type 1 and Type 2, then support you through the audit.
Certified ISO/IEC 27001:2022 (certificate IN60432E)
See the engagement path, 6 phasesSee the full Compliance service index
Key facts
SOC 2 at a Glance
- Report types
- A Type 1 report judges control design at a single point in time. A Type 2 report tests that the controls operated effectively across a period.
- Observation period
- Usually three to twelve months; three to six for a first report, and our six to nine months to a first Type 2 assumes three.
- Our role
- Criteria selection, gap assessment, control design, evidence automation, and representing you through the auditor's fieldwork.
- What we are not
- SecureRoot Risk Advisory LLP is not a CPA firm and cannot issue the SOC 2 report. One of our partner CPA firms does, independent of our readiness work.
- Time to first report
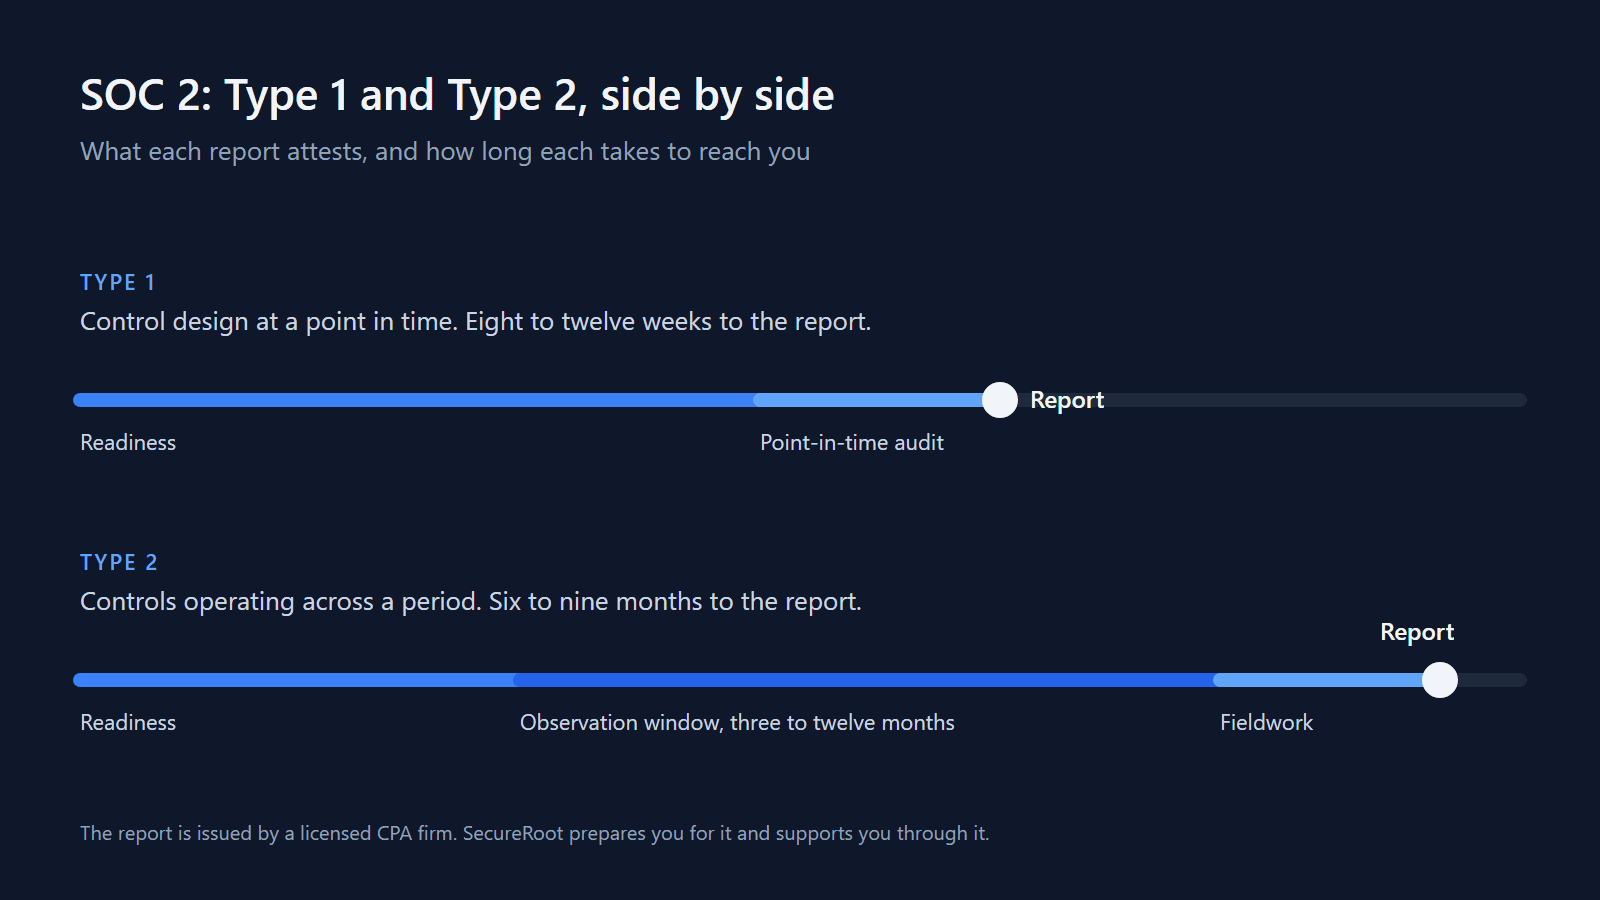
- Eight to twelve weeks to a Type 1, and six to nine months to a first Type 2.
- Price
- ₹1.5 lakh to ₹4.5 lakh for readiness and audit support, the same for either report type. The CPA firm's fee is separate and you contract with them directly.
Reviewed by Sachin Shirish, Director, CEH (EC-Council), ISO 27001 Lead Auditor
Reviewed by Pragya Dwivedi, Associate Director, CISM (ISACA), eWPTX (INE Security)
In short
How much does SOC 2 cost in India, how long does it take, and who issues the report?
Indicative range: ₹1.5 lakh to ₹4.5 lakh ($1,600 to $4,700) for readiness and audit support. It is the same whether the report is Type 1 or Type 2. The quote depends on the Trust Services Criteria you include and how much of the control set exists. For Type 2, the observation period's length also counts. Expect eight to twelve weeks to a Type 1. A first Type 2 takes six to nine months, assuming a three month observation window. SecureRoot is not a CPA firm and cannot issue the SOC 2 report. One of our partner CPA firms does, independently of our readiness work. The auditor's fee is separate and you contract with them directly. The other cost outside our figure is your own team's time across the observation window, producing evidence month after month. We confirm a fixed price once scoping is done, never before.
Case study
A SaaS Platform Reaches SOC 2 Type II on the First Attempt
- 0 Audit Exceptions
- 16 weeks To Audit Ready
Fintech, NBFC or payment aggregator? RBI testing duties, direct or through a partner, run alongside SOC 2. See VAPT for banks, NBFCs and fintechs or PCI DSS for payment aggregators.
Type 1 or Type 2
Type 1 or Type 2, and Year One
| Type 1 | Type 2 | |
|---|---|---|
| What the report attests | Control design at a point in time | Controls operating across a period |
| Observation window | None | Three to twelve months |
| Time to the report | Eight to twelve weeks | Six to nine months |
| SecureRoot readiness support | ₹1.5 lakh to ₹4.5 lakh | ₹1.5 lakh to ₹4.5 lakh |
| CPA audit fee, indicative | ₹2 lakh to ₹5 lakh | ₹5 lakh to ₹12 lakh |
| Year-one total, before platform fees | ₹3.5 lakh to ₹9.5 lakh | ₹6.5 lakh to ₹16.5 lakh |
The CPA firm invoices you directly.
SOC 2 Overview
SOC 2 is a licensed auditor's attestation on how well your controls meet the Trust Services Criteria. Security is always in scope. Availability, confidentiality, processing integrity and privacy are optional. Buyers use it to vet vendors quickly. We help Indian SaaS and IT services companies design controls, pick the right criteria and collect the evidence an auditor needs. We work remotely across India from our Greater Noida and Kanpur offices.
Methodology
How the SOC 2 Engagement Runs
Every phase has a named output, so you always know what is being worked on and what lands on your side of the table.
6 Phases, 6 Named Handovers
Flow
Flow chart of the SOC 2 engagement, 6 phases in order, each one selectable. Phase 1, Scoping and Criteria Selection. We choose which Trust Services Criteria apply and decide whether to start with a Type 1 or go straight to Type 2. Activities: Select the Trust Services Criteria in scope; Decide the Type 1 or Type 2 path and timing; Define system boundaries for the report; Introduce our partner CPA firms and align on timeline. Hands over Scope Memo and Audit Roadmap. Phase 2, Gap Assessment. We measure your controls against the criteria and give you a clear list of what to fix before the audit. Activities: Map existing controls to each criterion; Interview engineering, HR, and IT control owners; Test key controls for design and evidence; Rank gaps by audit impact and effort. Hands over Readiness Assessment Report. Phase 3, Control Design and Remediation. We help you design and implement the controls, from access reviews to change management and monitoring. Activities: Draft policies for access, change, and incidents; Implement quarterly access reviews; Stand up change management and monitoring controls; Assign owners for every control in the matrix. Hands over Control Matrix and Remediated Control Set. Phase 4, Evidence Automation. We connect a compliance platform so evidence collects itself. A Type 2 observation period depends on it. Activities: Connect cloud, HR, and code repositories to the platform; Map automated tests to each control; Set alerts for failing evidence checks; Close manual evidence gaps with owners. Hands over Automated Evidence Collection Setup. Phase 5, Observation Period Support. For Type 2, we help you run the controls consistently across the audit window and watch for drift. Activities: Monitor control performance across the window; Review platform alerts and fix drift early; Document exceptions and remediation; Run monthly check-ins with control owners. Hands over Clean Observation Period Evidence Trail. Phase 6, Audit Support. We work alongside your auditor through fieldwork so the report lands without surprises. Activities: Manage auditor evidence requests; Prepare control owners for walkthroughs; Respond to exceptions before they become findings; Review the draft report and management assertion. Hands over Closed Auditor Requests. Each phase begins from the artefact the phase before it produced.
Phase 01 Scoping and Criteria Selection
We choose which Trust Services Criteria apply and decide whether to start with a Type 1 or go straight to Type 2.
What Happens In This Phase
- Select the Trust Services Criteria in scope
- Decide the Type 1 or Type 2 path and timing
- Define system boundaries for the report
- Introduce our partner CPA firms and align on timeline
The Handover
Scope Memo and Audit Roadmap
The next phase starts from this.
Phase 01 Scoping and Criteria Selection
We choose which Trust Services Criteria apply and decide whether to start with a Type 1 or go straight to Type 2.
What Happens In This Phase
- Select the Trust Services Criteria in scope
- Decide the Type 1 or Type 2 path and timing
- Define system boundaries for the report
- Introduce our partner CPA firms and align on timeline
The Handover
Scope Memo and Audit Roadmap
The next phase starts from this.
- 01
Scoping and Criteria Selection
We choose which Trust Services Criteria apply and decide whether to start with a Type 1 or go straight to Type 2.
OutputScope Memo and Audit RoadmapActivities
- Select the Trust Services Criteria in scope
- Decide the Type 1 or Type 2 path and timing
- Define system boundaries for the report
- Introduce our partner CPA firms and align on timeline
- 02
Gap Assessment
We measure your controls against the criteria and give you a clear list of what to fix before the audit.
OutputReadiness Assessment ReportActivities
- Map existing controls to each criterion
- Interview engineering, HR, and IT control owners
- Test key controls for design and evidence
- Rank gaps by audit impact and effort
- 03
Control Design and Remediation
We help you design and implement the controls, from access reviews to change management and monitoring.
OutputControl Matrix and Remediated Control SetActivities
- Draft policies for access, change, and incidents
- Implement quarterly access reviews
- Stand up change management and monitoring controls
- Assign owners for every control in the matrix
- 04
Evidence Automation
We connect a compliance platform so evidence collects itself. A Type 2 observation period depends on it.
OutputAutomated Evidence Collection SetupActivities
- Connect cloud, HR, and code repositories to the platform
- Map automated tests to each control
- Set alerts for failing evidence checks
- Close manual evidence gaps with owners
- 05
Observation Period Support
For Type 2, we help you run the controls consistently across the audit window and watch for drift.
OutputClean Observation Period Evidence TrailActivities
- Monitor control performance across the window
- Review platform alerts and fix drift early
- Document exceptions and remediation
- Run monthly check-ins with control owners
- 06
Audit Support
We work alongside your auditor through fieldwork so the report lands without surprises.
OutputClosed Auditor RequestsActivities
- Manage auditor evidence requests
- Prepare control owners for walkthroughs
- Respond to exceptions before they become findings
- Review the draft report and management assertion
Specification
SOC 2: What We Run, and What We Measure You Against
The tooling our engineers use on this work, and the published standards the findings and evidence are mapped to.
Built by SecureRoot
TrustGrid
Our own GRC platform. Control mapping, evidence collection, policy workflow and third-party risk, all in one place.
What Is Examined, and What it Is Measured Against
Map
Map of the SOC 2 scope, running left to right in three stages. Stage one, what we run, 8 tools and techniques: Vanta, Drata, Sprinto, Scrut, Secureframe, AWS Config, Jira, Confluence. Stage two, findings from all of it are proven by hand and written up once. Stage three, measured against 5 published standards: AICPA Trust Services Criteria, SOC 2 Type 1, SOC 2 Type 2, AICPA SSAE 18, COSO Framework.
What We Run
8 tools
- Vanta
- Drata
- Sprinto
- Scrut
- Secureframe
- AWS Config
- Jira
- Confluence
Converges On
One Set of Proven Findings
Every issue is reproduced by hand before it is written down, and it is written down once.
Measured Against
5 standards
- SOC2AICPATrust Services Criteria
- SOC2AICPAType 1
- SOC2AICPAType 2
- AICPASSAE 18
- COSOFramework
Deliverables
SOC 2: What You Receive
- Readiness assessment report
- Control matrix mapped to criteria
- Remediation plan
- Evidence collection setup
- Audit support through fieldwork
Scope This Engagement
Tell us about your environment, your timelines and any audit dates you are working to. We come back with scope, effort and a start date.
Credentials
What We Hold, and What It Covers
What the Firm Holds
- ISO/IEC 27001:2022
- Certificate IN60432E, certification body Staunchly Management & System Services Private Limited
- SecureRoot's own information security management system is certified. It is a certificate about how we run our firm, not a certificate for your systems, and working with us does not confer it on you.
- ISO 9001:2015
- Certified quality management system
- SecureRoot's own quality management system is certified. Like the certificate above, it is about the firm itself and is not an assessment of any client.
Partner CPA Firms Issue the Report
Only a licensed CPA firm, working under the AICPA attestation standards, can issue a SOC 2 report, and it has to stay independent of whoever designed and implemented the controls. SecureRoot does not issue the report itself: it is issued by one of our partner CPA firms, introduced during scoping, and you choose between them.
What we do is everything on either side of the audit: scoping the criteria, closing the gaps, setting up evidence collection and supporting you through the partner firm's fieldwork. The report carries the auditor's name.
What It Costs
Indicative Ranges, Before You Ask
Every figure below is an indicative range, not a quote. Where you land in it depends on scope, and we confirm a fixed price only once scoping is done.
- Indicative rangeDepends on scope
SOC 2 Type 1 or Type 2
₹1.5 lakh to ₹4.5 lakh
Range as of 2 September 2026
$1,600 to $4,700
US dollar range as of 2 October 2026
What sets the figure
- Readiness and audit support for a Type 1 report on control design at a point in time, or a Type 2 report on controls operating over an observation period
- Security is always in scope; each optional Trust Services Criterion you add moves you up the range
- How much of the control set and evidence trail already exists, and for Type 2 the length of the observation window, set where you land in the range
Indicative ranges in INR, with a US dollar range where one is shown; the final quote depends on scope, and each range is dated on its own card.
Every band, third-party fees separate, is on the pricing page.
Get a Fixed Price for Your Scope
Tell us what is in scope and when you need it. You get a written scope and a fixed price, not a band.
Free Checklist
Get the SOC 2 Checklist
Our SOC 2 checklist: the controls, evidence and decisions the programme turns on, marked up for your scope. Tell us where to send it.
One form, the same notice as every enquiry on this site.
Should we start with SOC 2 Type 1 or Type 2?
Type 1 judges whether your controls are designed correctly at a single point in time. It is faster, and it unblocks a deal waiting on paperwork. Type 2 tests whether those controls actually operated across a period, usually three to twelve months. Buyers weigh it far more heavily, because design without operation proves very little. The common path is Type 1 first, then a Type 2 covering the months that follow. That lets you show progress while the observation window runs. Going straight to Type 2 makes sense when no deal is blocked and your control set is already mature. What decides it is usually commercial. How soon does a customer need the report, and which type will they accept?
How long is the Type 2 observation period?
Usually three to twelve months. A first report commonly uses a three to six month window. The annual reports that follow cover a full twelve months, leaving no gap for a customer to ask about. The window is a real constraint. Your controls have to run consistently across it, and evidence has to accumulate as you go. An auditor sampling month two cannot be satisfied with evidence produced in month six. That is why we connect a compliance platform during the evidence automation phase. Collection then happens without somebody remembering to do it. During the window we monitor control performance and fix drift early. We document any exception with its remediation and run a monthly check-in with each control owner. The auditor receives a continuous evidence trail.
Which Trust Services Criteria do we need?
Security, the common criteria, is always required and is the whole scope for most first reports. Availability, confidentiality, processing integrity and privacy are optional, added when you have made a promise that needs evidencing. Availability suits a platform selling on an uptime commitment. Confidentiality suits one handling customer data under contractual restrictions. Processing integrity matters where the correctness of a transaction is the product, as in payments or payroll. Privacy overlaps heavily with the DPDP Act and GDPR work you may already be doing. Each criterion you add brings more controls, more evidence and a longer audit. So include what your customers actually ask about, not everything that sounds reassuring. SecureRoot checks your contracts and security questionnaires during scoping and recommends the smallest set that answers them.
Does an Indian company need SOC 2?
No Indian law requires it. The DPDP Act, the RBI and SEBI directions and the CERT-In rules set their own obligations. None of them names SOC 2. The need is commercial. If you sell to US customers, their procurement and security teams ask for a SOC 2 report before they sign. Increasingly, so do buyers in the United Kingdom, the Gulf and Australia. Indian enterprise buyers ask far less often and usually accept ISO 27001 instead. So the test is your pipeline, not your geography. An Indian SaaS company with US customers needs SOC 2. A firm selling only to Indian banks may never be asked. During scoping SecureRoot tells you plainly whether SOC 2, ISO 27001 or both is the right first spend.
Who issues the SOC 2 report, and can SecureRoot issue it?
Only a licensed CPA firm, working under the AICPA attestation standards, can issue a SOC 2 report. It has to stay independent of whoever designed and implemented the controls. SecureRoot is not a CPA firm and cannot issue the report. No readiness consultant honestly can. A firm offering to build your controls and then attest to them is proposing an audit of its own work. We scope the criteria, close the gaps and set up evidence collection. Then we represent you through fieldwork, handling the auditor's requests and preparing your control owners for walkthroughs. We introduce our partner CPA firms during scoping: India-based practices and international firms that audit Indian SaaS companies remotely. You choose between them, so the auditor's fee and timeline are known before you commit.
Can we see a sample report or speak to the lead before we sign?
Yes, on request, and before anything is signed. SecureRoot names the engagement lead who will run your programme and puts them on the scoping call, not an account manager. We send a redacted sample report. You can judge the depth of a finding, its evidence and the remediation guidance against what you are paying for. A reference is the one thing we ask for rather than promise. We ask the client whose work most resembles yours whether they will take a call. No name is passed on before they say yes. Where nobody is available we offer a walkthrough of a delivered engagement with identifying details removed. None of this is published here, because our clients decide what is said about their work.
Primary Sources
Where the Figures on This Page Come From
Figures and requirements above are taken from the sources below, linked to the primary text wherever one exists rather than to a summary of it.
- 2017 Trust Services Criteria for Security, Availability, Processing Integrity, Confidentiality, and Privacy (with revised points of focus, 2022)
AICPA and CIMA · Link checked 2026-10-16
Related Reading
Articles on SOC 2
- SOC 2 Audit Process in India: Readiness, the Audit and How an Engagement Runs
- SOC 2 Attestation Cost in India: 2026 Pricing Breakdown
- How to Choose a SOC 2 Consultant: What They Do and What to Ask
- SOC 2 Type 1 vs Type 2 for Indian Companies: Which to Get First
- SOC 2 Trust Services Criteria Explained
- SOC 1 vs SOC 2: Which Report You Need
- How to Choose a SOC 2 Auditor
- SOC 2 and DPDPA Compliance
- What Is SOC 2 Compliance? A Plain Answer
- How Long Does SOC 2 Take? Type 1 and Type 2 Timelines
- ISO 27001 vs SOC 2: Which Framework Do You Need?
Read First
Before You Shortlist Anyone
- Compare SOC 2 Consulting Firms in IndiaSeven criteria, each firm checked against them, SecureRoot included.
- Who Can Sign Your Security ReportThe four signatures a buyer may want, and who can give each.
- SOC 2 Compliance Services in Delhi NCRLine-by-line costs, and the two timelines people confuse.
- SOC 2 Compliance Services in Noida and Greater NoidaA week-by-week calendar, from an office near Noida.
Keep Moving Through Compliance
Service 8 of 13 in this practice area
Practice Area
More in Compliance
- ISO 27001Build and certify your information security management system.
- ISO 27701Build a certifiable privacy information management system.
- ISO 22301Certify how your business keeps running through disruption.
- ISO 42001Govern your AI systems with the first AI management standard.
- DPDP ActGet ready for India's Digital Personal Data Protection Act.
- PCI DSSProtect cardholder data and pass your PCI assessment.
- HIPAAProtect health information and meet HIPAA requirements.
- CCPAMeet California's consumer privacy requirements.
- GDPRMeet Europe's data protection standard with confidence.
- NEN 7510Certify information security for Dutch healthcare.
- EU AI ActPrepare for Europe's risk-based AI regulation.
- Third Party Risk Assessment (TPRM)Understand and manage the risk your vendors bring.
- SOC 2 Penetration TestingCompliance Testing