Meet the DPDP Act
DPDP Act Compliance and Readiness Services in India
The DPDP Act is India's personal data protection law. It reaches any organisation that processes the digital personal data of people in India. We help you find where that data lives, close the gaps, and stand up the consent, rights and breach processes the Act expects. Most organisations complete the six phases in thirteen to twenty three weeks. There is no DPDP certificate in Indian law and no accredited DPDP certification body. So no firm, SecureRoot Risk Advisory LLP included, can certify DPDP compliance. It is self-accountable, and the Data Protection Board assesses it if it has cause to. SecureRoot is not a CERT-In empanelled auditing organisation and not a law firm. Legal opinions and representation before the Board stay with your counsel. Our pricing page gives guide ranges. A startup under ten thousand users starts from ₹1.5 lakh. An SME or mid-size company is ₹1.5 lakh to ₹8 lakh. A large enterprise with subsidiaries and complex flows is ₹15 lakh to ₹60 lakh. We scope first, then quote a fixed price in writing.
See the engagement path, 6 phasesSee the full Compliance service index
Key facts
DPDP Act at a Glance
- Who it applies to
- Any organisation processing the digital personal data of people in India, from India or from abroad, with no revenue or headcount threshold to fall below.
- Programme duration
- Six phases, which most organisations complete in thirteen to twenty three weeks.
- Gap assessment
- Inside the full programme, two to three weeks (one to two for a startup), after two to three weeks of data discovery. Bought on its own, by scale: under two weeks for a startup, three to five weeks for an SME, four to six for a mid-size estate and six to ten for a large enterprise, as on our pricing page.
- No certificate exists
- There is no DPDP certificate in Indian law and no accredited DPDP certification body. So no firm, SecureRoot included, can certify DPDP compliance.
- Who assesses compliance
- DPDP compliance is self-accountable. You are responsible for meeting the Act, and the Data Protection Board of India assesses that if it has cause to.
- What we are not
- SecureRoot is not a CERT-In empanelled auditing organisation and not a law firm. Legal opinions, filings and representation before the Board stay with your counsel.
- Maximum penalty
- Up to 250 crore rupees for failing to take reasonable security safeguards against a personal data breach. The Data Protection Board assesses it per contravention.
- Price
- Guide ranges, as on our pricing page. Startup under ten thousand users: from ₹1.5 lakh. SME or mid-size company: ₹1.5 lakh to ₹8 lakh. Large enterprise: ₹15 lakh to ₹60 lakh. We scope first, then quote a fixed price in writing.
- Commencement
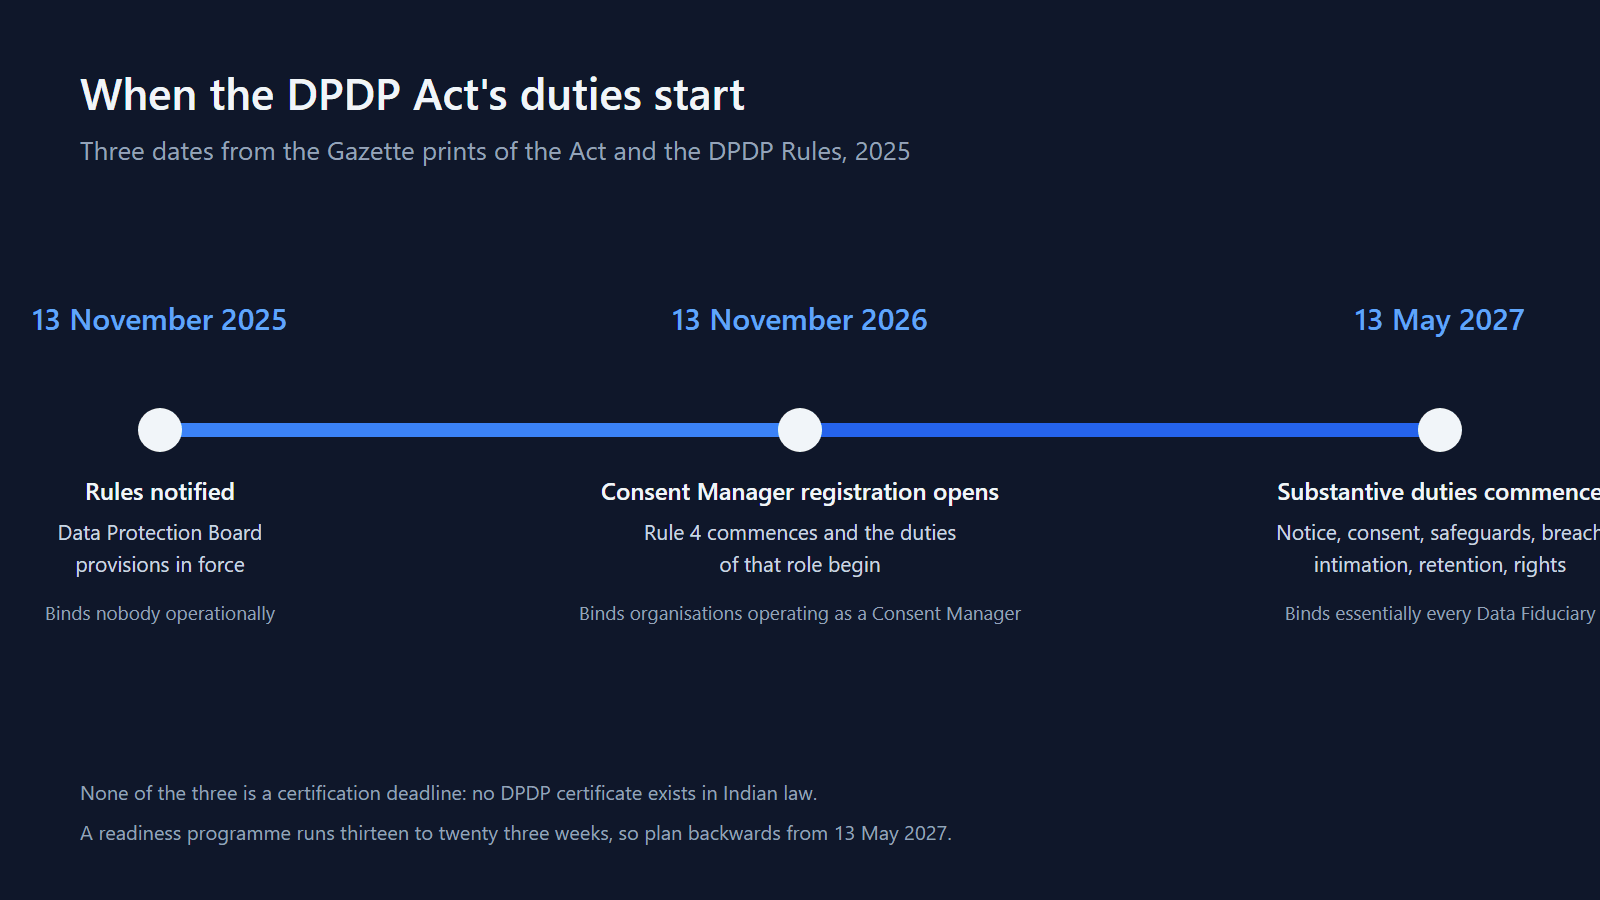
- Rules notified 13 November 2025. Consent Manager provisions from 13 November 2026. Most Data Fiduciary duties from 13 May 2027.
Reviewed by Sachin Shirish, Director, CEH (EC-Council), ISO 27001 Lead Auditor
Reviewed by Pragya Dwivedi, Associate Director, CISM (ISACA), eWPTX (INE Security)
In short
How much does DPDP Act readiness cost, how long does it take, and who certifies it?
SecureRoot's DPDP Act readiness programme runs six phases over thirteen to twenty three weeks for most organisations. The phases are data discovery and mapping, the gap assessment against the Act and its Rules, consent and notice design, rights and breach processes, control implementation, and a readiness review. The range is wide. It moves with how many systems hold personal data and how much of your security control set already exists. Our pricing page sets guide ranges by size. A startup under ten thousand users starts from ₹1.5 lakh. An SME or mid-size company is ₹1.5 lakh to ₹8 lakh, and a large enterprise ₹15 lakh to ₹60 lakh. We scope first, then quote a fixed price in writing. Nobody signs a certificate at the end. There is no DPDP certificate in Indian law and no accredited DPDP certification body. So no firm, SecureRoot included, can certify DPDP compliance.
Case study
A Hospital Network Builds DPDP Act Readiness Across 12 Facilities
Fintech, NBFC or payment aggregator? RBI testing duties, direct or through a partner, run alongside the DPDP Act. See VAPT for banks, NBFCs and fintechs or PCI DSS for payment aggregators.
Commencement
When the DPDP Act's Duties Start
| Date | What commences | Who it binds |
|---|---|---|
| 13 November 2025 | Rules notified; Data Protection Board provisions in force | Nobody operationally |
| 13 November 2026 | Consent Manager registration opens | Consent Managers only |
| 13 May 2027 | Notice, consent, safeguards, breach intimation, retention, rights | Essentially every Data Fiduciary |
DPDP Act Overview
The DPDP Act governs how organisations collect, use and protect the personal data of people in India. Its duties cover consent, notice, data principal rights and breach reporting, backed by real penalties. It applies to almost anyone handling Indian personal data.
Methodology
How the DPDP Act Engagement Runs
Every phase has a named output, so you always know what is being worked on and what lands on your side of the table.
6 Phases, 6 Named Handovers
Flow
Flow chart of the DPDP Act engagement, 6 phases in order, each one selectable. Phase 1, Data Discovery and Mapping. We map where personal data enters, flows, and rests across your systems. You cannot protect what you have not found. Activities: Scan systems and databases for personal data; Interview teams on collection and sharing points; Map data flows across vendors and borders; Build the personal data inventory. Hands over Data Flow and Inventory Map. Phase 2, Gap Assessment Against the DPDP Act. We measure your current practices against the DPDP Act and its Rules, covering consent, notice, and data principal rights. Activities: Assess consent and notice practices against the Act; Review readiness for data principal rights; Check breach reporting and security safeguards; Rank gaps by penalty exposure and effort. Hands over DPDP Act Gap Assessment Report. Phase 3, Consent and Notice Design. We help you build clear notices and a consent mechanism that meets the law, including consent manager considerations. Activities: Draft notices in plain language per purpose; Design the consent capture and withdrawal flow; Assess consent manager integration options; Plan notice delivery in the required languages. Hands over Consent and Notice Framework. Phase 4, Rights and Breach Processes. We set up processes for data principal requests and for reporting breaches within the required timelines. Activities: Build the data principal request workflow; Define grievance redressal roles and timelines; Write the breach notification procedure; Run a breach response tabletop exercise. Hands over Data Principal Rights Playbook and Breach Procedure. Phase 5, Control Implementation. We help you put in place the security safeguards and retention rules the DPDP Act expects. Activities: Implement encryption and access safeguards; Set retention and erasure schedules; Update processor contracts with DPDP Act clauses; Roll out privacy training to data-handling teams. Hands over Implemented Safeguards and Retention Schedule. Phase 6, Readiness Review. We run a final review so you can show a regulator, or a customer, that your programme holds together. Activities: Test the consent and rights workflows end to end; Verify remediation of earlier gaps; Compile the accountability evidence pack; Brief leadership on residual risk. Hands over DPDP Act Readiness Report. Each phase begins from the artefact the phase before it produced.
Phase 01 Data Discovery and Mapping
We map where personal data enters, flows, and rests across your systems. You cannot protect what you have not found.
What Happens In This Phase
- Scan systems and databases for personal data
- Interview teams on collection and sharing points
- Map data flows across vendors and borders
- Build the personal data inventory
The Handover
Data Flow and Inventory Map
The next phase starts from this.
Phase 01 Data Discovery and Mapping
We map where personal data enters, flows, and rests across your systems. You cannot protect what you have not found.
What Happens In This Phase
- Scan systems and databases for personal data
- Interview teams on collection and sharing points
- Map data flows across vendors and borders
- Build the personal data inventory
The Handover
Data Flow and Inventory Map
The next phase starts from this.
- 01
Data Discovery and Mapping
We map where personal data enters, flows, and rests across your systems. You cannot protect what you have not found.
OutputData Flow and Inventory MapActivities
- Scan systems and databases for personal data
- Interview teams on collection and sharing points
- Map data flows across vendors and borders
- Build the personal data inventory
- 02
Gap Assessment Against the DPDP Act
We measure your current practices against the DPDP Act and its Rules, covering consent, notice, and data principal rights.
OutputDPDP Act Gap Assessment ReportActivities
- Assess consent and notice practices against the Act
- Review readiness for data principal rights
- Check breach reporting and security safeguards
- Rank gaps by penalty exposure and effort
- 03
Consent and Notice Design
We help you build clear notices and a consent mechanism that meets the law, including consent manager considerations.
OutputConsent and Notice FrameworkActivities
- Draft notices in plain language per purpose
- Design the consent capture and withdrawal flow
- Assess consent manager integration options
- Plan notice delivery in the required languages
- 04
Rights and Breach Processes
We set up processes for data principal requests and for reporting breaches within the required timelines.
OutputData Principal Rights Playbook and Breach ProcedureActivities
- Build the data principal request workflow
- Define grievance redressal roles and timelines
- Write the breach notification procedure
- Run a breach response tabletop exercise
- 05
Control Implementation
We help you put in place the security safeguards and retention rules the DPDP Act expects.
OutputImplemented Safeguards and Retention ScheduleActivities
- Implement encryption and access safeguards
- Set retention and erasure schedules
- Update processor contracts with DPDP Act clauses
- Roll out privacy training to data-handling teams
- 06
Readiness Review
We run a final review so you can show a regulator, or a customer, that your programme holds together.
OutputDPDP Act Readiness ReportActivities
- Test the consent and rights workflows end to end
- Verify remediation of earlier gaps
- Compile the accountability evidence pack
- Brief leadership on residual risk
Specification
DPDP Act: What We Run, and What We Measure You Against
The tooling our engineers use on this work, and the published standards the findings and evidence are mapped to.
Built by SecureRoot
DPDPA Autopilot
Our own privacy platform. Consent, notices, data principal requests and records of processing under the DPDP Act.
What Is Examined, and What it Is Measured Against
Map
Map of the DPDP Act scope, running left to right in three stages. Stage one, what we run, 7 tools and techniques: OneTrust, Securiti, TrustArc, Microsoft Purview, BigID, Jira, Confluence. Stage two, findings from all of it are proven by hand and written up once. Stage three, measured against 5 published standards: Digital Personal Data Protection Act, 2023, Digital Personal Data Protection Rules, 2025, ISO/IEC 27701:2025, ISO/IEC 27001:2022, NIST Privacy Framework.
What We Run
7 tools
- OneTrust
- Securiti
- TrustArc
- Microsoft Purview
- BigID
- Jira
- Confluence
Converges On
One Set of Proven Findings
Every issue is reproduced by hand before it is written down, and it is written down once.
Measured Against
5 standards
- Digital Personal Data Protection Act, 2023
- Digital Personal Data Protection Rules, 2025
- ISO/IEC 27701:2025
- ISO/IEC 27001:2022
- NIST Privacy Framework


Deliverables
DPDP Act: What You Receive
- Data flow and inventory map
- DPDP Act gap assessment report
- Consent and notice framework
- Data principal rights playbook
- Breach response procedure
Scope This Engagement
Tell us about your environment, your timelines and any audit dates you are working to. We come back with scope, effort and a start date.
Free Checklist
Get the DPDP Act Checklist
Our DPDP Act checklist: the controls, evidence and decisions the programme turns on, marked up for your scope. Tell us where to send it.
One form, the same notice as every enquiry on this site.
If you want a first read on where you stand before you talk to anyone, try our free DPDPA gap assessment: a self-assessment against the DPDP Act 2023 and the DPDP Rules 2025 covering 19 controls in 7 areas, with a risk analysis, a gap report and evidence uploads. Registration is free. It is not an audit, a certificate or legal advice.
DPDP Act guides for Noida, Greater Noida, Delhi, Gurugram and Ghaziabad.
Who does the DPDP Act apply to?
The Act applies to any organisation that processes the digital personal data of people in India, from India or abroad. If you sit outside India and offer goods or services to people in India, you are still in scope. In the Act's language you are a data fiduciary, the entity that decides why and how personal data is processed. Processors who handle data on your behalf are covered through the contract you hold with them. There is no revenue or headcount threshold to fall below. A twenty person SaaS company and a listed bank are both in scope. What differs is the depth of programme each needs. Purely personal or domestic processing sits outside the Act, as does data the data principal has themselves made publicly available.
What is a data principal under the DPDP Act?
A data principal is the individual the personal data belongs to, the term the Act uses where GDPR says data subject. Under the Act they can ask what data you hold and who you have shared it with. They can have it corrected, completed or erased. They can nominate someone to exercise their rights if they die or become incapacitated. They also get a grievance redressal route that actually answers them. You need a channel for requests and a way to find that person's data in every system holding it. You also need a defined turnaround you can evidence. Where a child's data is involved you also need verifiable parental consent. SecureRoot builds the request workflow and the audit trail that shows you honoured it.
What penalties does the DPDP Act carry?
The Schedule to the Act sets the penalties the Data Protection Board of India can impose. They are assessed per contravention, not as a single annual cap. Failure to take reasonable security safeguards to prevent a personal data breach carries up to 250 crore rupees. Failure to notify the Board and the affected data principals of a breach carries up to 200 crore rupees. So does a breach of the additional obligations for children's data. Failure to meet the extra duties placed on a Significant Data Fiduciary carries up to 150 crore rupees. Any other contravention carries up to 50 crore rupees. The Board weighs the nature and gravity of the breach, whether it was repeated, and what you did to mitigate it. A working breach process reduces your exposure.
Do we need to appoint a Data Protection Officer?
Only if you are notified as a Significant Data Fiduciary. The government can designate you on the volume and sensitivity of the data you process and the risk to data principals. Potential impact on India's sovereignty and integrity, and on electoral democracy, also counts. If designated, you must appoint a Data Protection Officer based in India who reports to your board or governing body. You must also appoint an independent data auditor and run periodic Data Protection Impact Assessments. Every other data fiduciary still has to publish contact details for someone who can answer data principal questions. Many organisations appoint the role voluntarily because enterprise customers ask for it during due diligence. SecureRoot runs it as a service through our vDPO offering when you would rather not hire for it.
When do the DPDP Act's duties actually start?
In three steps, and the dates come from the Gazette prints cited under Primary Sources on this page. The DPDP Rules, 2025 were notified on 13 November 2025. The Consent Manager provisions apply from 13 November 2026, the date Consent Manager registration opens under Rule 4. Most of the duties a Data Fiduciary will feel in practice apply from 13 May 2027. That last date is the one to plan backwards from. A full readiness programme runs thirteen to twenty three weeks. A team starting after the end of 2026 is already inside the window. The audit-only route is for that case. None of the three is a certification deadline, because no DPDP certificate exists anywhere in Indian law today.
Can we see a sample report or speak to the lead before we sign?
Yes, on request, and before anything is signed. SecureRoot names the engagement lead who will run your programme and puts them on the scoping call, not an account manager. We send a redacted sample report. You can judge the depth of a finding, its evidence and the remediation guidance against what you are paying for. A reference is the one thing we ask for rather than promise. We ask the client whose work most resembles yours whether they will take a call. No name is passed on before they say yes. Where nobody is available we offer a walkthrough of a delivered engagement with identifying details removed. None of this is published here, because our clients decide what is said about their work.
Primary Sources
Where the Figures on This Page Come From
Figures and requirements above are taken from the sources below, linked to the primary text wherever one exists rather than to a summary of it.
- The Digital Personal Data Protection Act, 2023 - Gazette of India print (CG-DL-E-12082023-248045), including the Schedule of penalties
Ministry of Law and Justice, Government of India · Link checked 2026-11-03
- The Digital Personal Data Protection Rules, 2025 - G.S.R. 846(E), Gazette of India print (CG-DL-E-14112025-267650)
Ministry of Electronics and Information Technology, Government of India · Link checked 2026-11-03
Related Reading
Articles on DPDP Act
- SOC 2 and DPDPA Compliance
- DPDP Compliance Software in India: A Buyer's Guide to Tool Categories and Steps
- DPDP Act Compliance Checklist: 12 Steps After the 2025 Rules
- DPDP Compliance Deadline 13 May 2027: What to Do Now
- DPDP Act Penalties: What Each Breach Can Cost
- DPDPA vs GDPR: Key Differences Explained
- Who Is a Significant Data Fiduciary? A Plain Answer
- DPDP Act Breach Notification: What Applies Now and What Starts in 2027
- DPDP Gap Analysis in India: Find Your Compliance Gaps Fast
- DPDP Compliance Audit in India: Process, Checklist & Cost
- Consent Management Under India’s DPDP Act: A Practical Guide
- How to Choose a DPDP Consultant in India, and What One Does
- DPDP Consultant in Noida: A Local Engagement, Week by Week, and What It Costs
- Data Protection Officer Services in India: Do You Need a DPO?
Related Services
Often Scoped Alongside This
- vDPOA Data Protection Officer run as a service, when you are notified as a Significant Data Fiduciary or a customer asks for one before you want to hire.
- Consent HubOur consent management platform for Data Fiduciaries: itemised notices, a tamper-evident consent ledger and withdrawals pushed to connected systems. It is not a registered Consent Manager.
- DPDPA AutopilotThe six-phase readiness programme running as software: a dated plan, the Record of Processing Activities built from discovery, and readiness scored against a 68-row requirement mapping. A readiness aid, not legal advice.
Read First
Before You Shortlist Anyone
- DPDP Act Compliance Cost in IndiaWhat drives the number, the one-time cost against the annual run-rate, and why no two published figures agree.
- DPDP Compliance Companies in IndiaSeven criteria, every claim cited to the firm that published it, no scores, and the two criteria we fail.
- DPDP Consultants in Delhi NCRWho else ranks for Delhi, Gurugram and Noida, what each of them publishes, and the five cases where we are the wrong firm.
- DPDP Consultant in NoidaA local engagement, week by week, and what it costs.
- The DPDP Consent Manager DeadlineWhat 13 November 2026 starts, and why it is probably not the date your programme runs to.
- Privacy Assessment Scoping ChecklistMarkets, entities, data categories, flows, processors, notices and consent, ready before the call.
Keep Moving Through Compliance
Service 5 of 13 in this practice area
Practice Area
More in Compliance
- ISO 27001Build and certify your information security management system.
- ISO 27701Build a certifiable privacy information management system.
- ISO 22301Certify how your business keeps running through disruption.
- ISO 42001Govern your AI systems with the first AI management standard.
- PCI DSSProtect cardholder data and pass your PCI assessment.
- HIPAAProtect health information and meet HIPAA requirements.
- SOC 2Earn a SOC 2 report your customers can trust.
- CCPAMeet California's consumer privacy requirements.
- GDPRMeet Europe's data protection standard with confidence.
- NEN 7510Certify information security for Dutch healthcare.
- EU AI ActPrepare for Europe's risk-based AI regulation.
- Third Party Risk Assessment (TPRM)Understand and manage the risk your vendors bring.
- DPDP Act Security Testing and VAPTCompliance Testing